Skip to:
Content
Pages
Categories
Search
Top
Bottom

Search Results for 'wordpress'

Viewing 25 results - 18,751 through 18,775 (of 32,690 total)
  • Author
    Search Results
  • #132255
    aces
    Participant

    Wordpress Admin Settings > General > Membership – select Anyone can register ?

    #28618
    benharvey29
    Member

    Hi,

    I’m new to Buddypress development and I’m looking to add a button on the page that displays a list of topics within a forum. Creating the markup to create the button that jumps to the form at the bottom of the page is no problem, but I am struggling to find where to modify the template to add the button.

    From what I understand, the forum pages use the default ‘page.php’ template from the active wordpress theme. Is there a way to detect when you are on this type of page using some sort of method from buddypress i.e. is_forum_page()?

    If this method is not available, can someone point me in the direction of the code within the buddypress plugin that outputs the content, so that I can modify the output?

    Apologies if this has already been covered or if I’m missing the point, but I’ve struggled to find an answer to this problem through the forums.

    Thanks v much in advance.

    #132243
    Paul Wong-Gibbs
    Keymaster

    After spending an hour trying things, I’ve discovered that if you’re on https, the user avatar includes are always http.

    EDIT: Made a ticket https://buddypress.trac.wordpress.org/ticket/4110

    #132239
    aces
    Participant

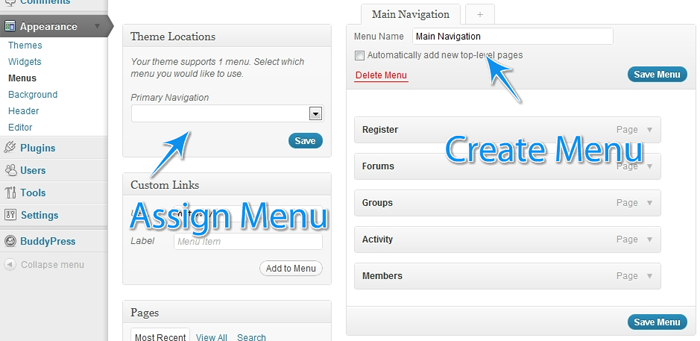
    You need to create both menus. Without it wordpress has it’s own default menu which you have been relying on

    A good guide for understanding wordpress menus is http://justintadlock.com/archives/2010/06/01/goodbye-headaches-hello-menus

    #132238
    DRAGUIAN
    Member

    It’s frustrating because that’s almost it. I leave the Header navigation as blank because my buddypress/wordpress pages automatically fill in that menu. So when I am logged in all the pages I want to see are there. I only made my homepage and about page available to the nonmembers, and that works fine too. However, when a user is logged off, they can still see all the pages available to a logged in user aswell as the pages which are available to them. So instead of having one smooth menu for the non member, theres the members menu and below it a non members menu. Note this is only for logged out members everything is fine as far as signed in users are concerned.

    #132235
    DRAGUIAN
    Member

    OK alternative menu etc is all set up on menus page. I am using the Elbee Elgee child theme at the moment. Do I still have to do the first step of implementing that code in the headers menu (<?php
    // https://codex.wordpress.org/Function_Reference/wp_get_current_user
    $current_user = wp_get_current_user();……

    #132234
    aces
    Participant

    You should make a child of bp-default and backup files and db just in case…

    You don’t add or remove any pages from the code. The point is that it works from the built in wordpress default menu system. ( https://codex.wordpress.org/Navigation_Menus )

    To get the second menu to appear – In your child theme’s functions.php file add:
    `function register_my_menus() {
    register_nav_menus( array(
    ‘primary’ => __( ‘Header Navigation’ ),
    ‘secondary-menu’ => __( ‘Alternative Menu’ ),
    ‘another-menu’ => __( ‘Another Menu’ )
    ) );
    }
    add_action( ‘init’, ‘register_my_menus’ );
    `

    #132229
    aces
    Participant

    You shouldn’t touch wp or bp core files.

    What theme are you using?

    In your child theme’s header.php file you replace the `wp_nav_menu` section with either of the above ( not both ).

    Then you can define two menus on appearance > menus ( primary and secondary-menu on the above example ) Set one for logged in users and one for everyone else.

    #132228
    PJ
    Participant

    Paul,

    Ideally I’d like to have the whole site forced https since I have a private ssl. So, WP+BP in all https if possible.

    I did a fresh install of WP and just installed BP, so I doubt it’s an image issue. Is there a way to go totally https?

    I also went to Settings > General and changed WordPress Address (URL) to have an https rather than http. Anytime I click BP parts of the site it goes back to regular http.

    #132225
    DRAGUIAN
    Member

    I am guessing that I need to make a change in the wordpress-includes pluggable.php

    #132223
    DRAGUIAN
    Member

    I prefer the first option of serving different menus whether the user is logged in or not. Should I put that code into the themes header or funtion.php? Do I need to add to the given code it to specify which pages I want to hide from logged out users. Using latest version of wordpress and buddypress

    #28608

    I have a site at ElliottAnalysis.com. When my site appears on other sites blog rolls, the rss of the site wide activity is displayed instead of the rss of the wordpress. I’m not sure why this is the case. I’ve been looking for a clue all over the place but no luck. Anyone can help on this. Much appreciated.

    #132220
    Paul Wong-Gibbs
    Keymaster

    You need to figure out and tell us what is being included over http. Also your WordPress and BuddyPress versions. Thanks.

    #28605
    PJ
    Participant

    I added

    `# BEGIN WordPress

    RewriteEngine On
    RewriteBase /
    RewriteCond %{REQUEST_FILENAME} !-f
    RewriteCond %{REQUEST_FILENAME} !-d
    RewriteRule . /index.php [L]
    RewriteEngine On
    RewriteCond %{SERVER_PORT} 80
    RewriteRule ^(.*)$ https://www.mysite.com/$1 [R,L]

    # END WordPress`

    To the .htaccess file and the entire site went https (I have a private SSL and dedicated IP).

    I installed/activated BuddyPress and the entire site has a broken https with the following message:
    Your connection to http://www.mysite.com is encrypted with 256-bit encryption. However, this page includes other resources which are not secure. These resources can be viewed by others while in transit, and can be modified by an attacker to change the behavior of the page.

    The connection uses TLS 1.0.

    The connection is encrypted using AES_256_CBC, with SHA1 for message authentication and DHE_RSA as the key exchange mechanism.

    The connection is not compressed.

    #132209

    In reply to: fake user signup

    @mercime
    Participant

    == how can they sign up to my database without filling in the recaptcha or confirming their mail? ==
    There is a possibility that your old BP1.2.7/WP3.2 installation has been hacked. I would start backing up DB and server files to your hard drive. See https://codex.wordpress.org/FAQ_My_site_was_hacked

    == but for some reason the search field always brings me to the homepage instead of search results. ==
    Yes we are aware of this and the issue will be resolved soon.

    #132205
    @mercime
    Participant

    == Using cpanel (fantastico) … how can i reinstall wordpress, can this be the issue? ==

    @allentan you will need to re-install WordPress. WordPress should be installed manually, e.g. via FTP, and NOT via webhost scripts which bring about numerous issues when BuddyPress is activated.” (reference)

    #132198
    @mercime
    Participant
    #132196
    shanebp
    Moderator

    Reported to developers and fixed in version 1.5.5

    czz
    Member

    Today the have released a sql injection for BP

    #132195
    aces
    Participant

    One way of doing that is by serving different menus depending whether someone is logged in or not such as
    `
    <?php
    // https://codex.wordpress.org/Function_Reference/wp_get_current_user
    $current_user = wp_get_current_user();
    if ( 0 == $current_user->ID ) {
    wp_nav_menu( array( ‘container’ => false, ‘menu_id’ => ‘nav’, ‘theme_location’ => ‘secondary-menu’, ‘fallback_cb’ => ” ) );
    // Not logged in.
    } else {
    wp_nav_menu( array( ‘container’ => false, ‘menu_id’ => ‘nav’, ‘theme_location’ => ‘primary’, ‘fallback_cb’ => ” ) );
    // Logged in.
    }
    ?>
    `
    or another approach:
    `
    <?php
    if ( is_user_logged_in() ) {
    wp_nav_menu( array( ‘container’ => false, ‘menu_id’ => ‘nav’, ‘theme_location’ => ‘primary’, ‘fallback_cb’ => ” ) );
    } else {
    wp_nav_menu( array( ‘container’ => false, ‘menu_id’ => ‘nav’, ‘theme_location’ => ‘secondary-menu’, ‘fallback_cb’ => ” ) );
    }
    ?>
    `
    replacing the `wp_nav_menu` bit in the ( child ) theme’s header.php file. It may need adapting depending on theme etc. Remember to make backups before editing!

    Then use the walled garden or similar techniques to redirect users if they try to reach the page directly…

    #28593
    harsha52
    Member

    I recently installed Buddypress plugin Version 1.5.5, And the WordPress version 3.3.1,

    I created 2 user a) user 1 (admin). b) user 2 (Normal user).

    User1(admin) will login and click on members tab it will take to the member page, i.e “http://localhost/projects/headstart/members/&#8221;

    if admin try to click on user1(admin) view Link (view his profile page), it takes to this URL “http://localhost/projects/headstart/members/headstart/activity/4 “

    Which is Error page,

    ![Error][1]

    ” Page not found We’re sorry, but we can’t find the page that you’re looking for. Perhaps searching will help.”

    Similarly User2(Normal user)will login, and click on members tab it will take to the member page , i.e “http://localhost/projects/headstart/members/&#8221;

    If Normal user try to click on user2(Normal user) view Link (view his profile page), it takes to this URL “http://localhost/projects/headstart/member/Normal user/”. which is working fine

    Can anyone please answer why is it throwing an error when admin tries to login and view his profile page ?

    #132181

    In reply to: Unified Profile Page?

    @ChrisClayton
    Participant

    @BossX – As in, similar to the wordpress profiles (https://profiles.wordpress.org/matt)?
    Yes, it’s possible through a custom theme.

    The top part with the profile information is simply the members/single/member-header.php file with code to insert their bio and other info – See: http://bp-tricks.com/snippets/displaying-certain-profile-fields-on-your-members-profile-page/

    The bottom part is the members/single/profile.php template (their activity is an external custom built activity stream, but the theory is the same… just add the activity loop) – See: https://codex.buddypress.org/developer-docs/custom-buddypress-loops/the-activity-stream-loop/

    And then they changed the default profile view from the activity view to profile with – define( ‘BP_DEFAULT_COMPONENT’, ‘profile’ );

    cpavel
    Member

    I think I resolved the issue. The issue was that only users that are on GMAIL receive new user activation email upon joining my buddypress powered site. Users in other email domains were not receiving user activation emails. I am running my own VPS based host, essentailly I own the server with public IP that is running WP and BP, so I think this situation might apply to others, hence this post. I am hoping this could help others with similar email issues.

    Here are the of my install:

    1. WordPress version 3.3.1
    2. WordPress installed as directory
    3. WordPress installed in root
    4. Fresh Install
    5. Fresh install of BP version 1.5.4 define( ‘BP_ENABLE_MULTIBLOG’, true);
    6. Running LEMP server (CentOS 5.8+Nginx +MySQL+PHP)

    7. Started troubleshooting by checking sendmail logs:
    cat /var/spool/mail/nginx

    8. Observed following error messages:


    The following addresses had permanent fatal errors


    (reason: 554 Denied [SHXBL] – Denied by Spamhaus XBL – See http://www.spamhaus.org/query/bl?ip=my.host.ip.add (Mode: normal))

    9. Followed link provided to spamhaus which presented me with:

    my.host.ip.add is listed in the XBL, because it appears in:

    CBL (link to CBL)

    10. Followed CBL Link to read:
    “This IP address is HELO’ing as “localhost.localdomain” which violates the relevant standards (specifically: RFC5321)”

    11. Followed link provided to http://cbl.abuseat.org/namingproblems.html
    the gist of which is:
    “There are two basic types of detections that land an IP in this page. RFC2821 section 4.1.1.1 says that there are only two legal types of HELO/EHLO a mail server can issue – either a fully qualified domain name (eg: “mail.example.com”) or an “IP literal” (eg: “[1.2.3.4]”).”

    12. Followed instructions to fix link for UNIX system (also there is a link for Windows) to http://cbl.abuseat.org/sendmailhelp.html

    13. completed fix to sendmail.cf file, I chose to respond to HELO as [my.host.ip.add] fashion and completed sendmail restart.

    14. you will now need to delist your domain from CBL – go back to CBL link (it will complain about timestamp, so might have to do it through spamhaus link) and at the bottom of the page there should be link to request de-listing. Click and wait 1-2 hours

    14. I tested again, by sending registration email from my BP install (signed up new user) to check how the email header is received now, here is a comparison for before and after. Then fix was confirmed working as registration email came through to another email domain

    Before:
    Received: from localhost.localdomain ([my.host.ip.add])
    by mx.google.com with ESMTP id e70si6268183yhk.134.2012.03.30.09.16.56;
    Fri, 30 Mar 2012 09:16:56 -0700 (PDT)

    After:
    Received: from [my.host.ip.add] ([my.host.ip.add])
    by mx.google.com with ESMTP id n5si4532434614yhm.135.2012.03.30.11.24.59;
    Fri, 30 Mar 2012 11:24:59 -0700 (PDT)

    #132180
    aces
    Participant

    I am also http://testbp.org/members/aces/ You should be able to pm me there, although I haven’t tested it with pm before and I’m not sure I can help…..

    Did you use an auto installer provided by your host to install wordpress and/or buddypress etc? Autoinstallers have been the cause of many problems in the past.

    Note

Viewing 25 results - 18,751 through 18,775 (of 32,690 total)
Skip to toolbar